CIPL’s Annual Summit 2026 brought our global community together for a day of discussion, collaboration and reflection. The event also marked 25 years of the Centre for Information Policy Leadership.
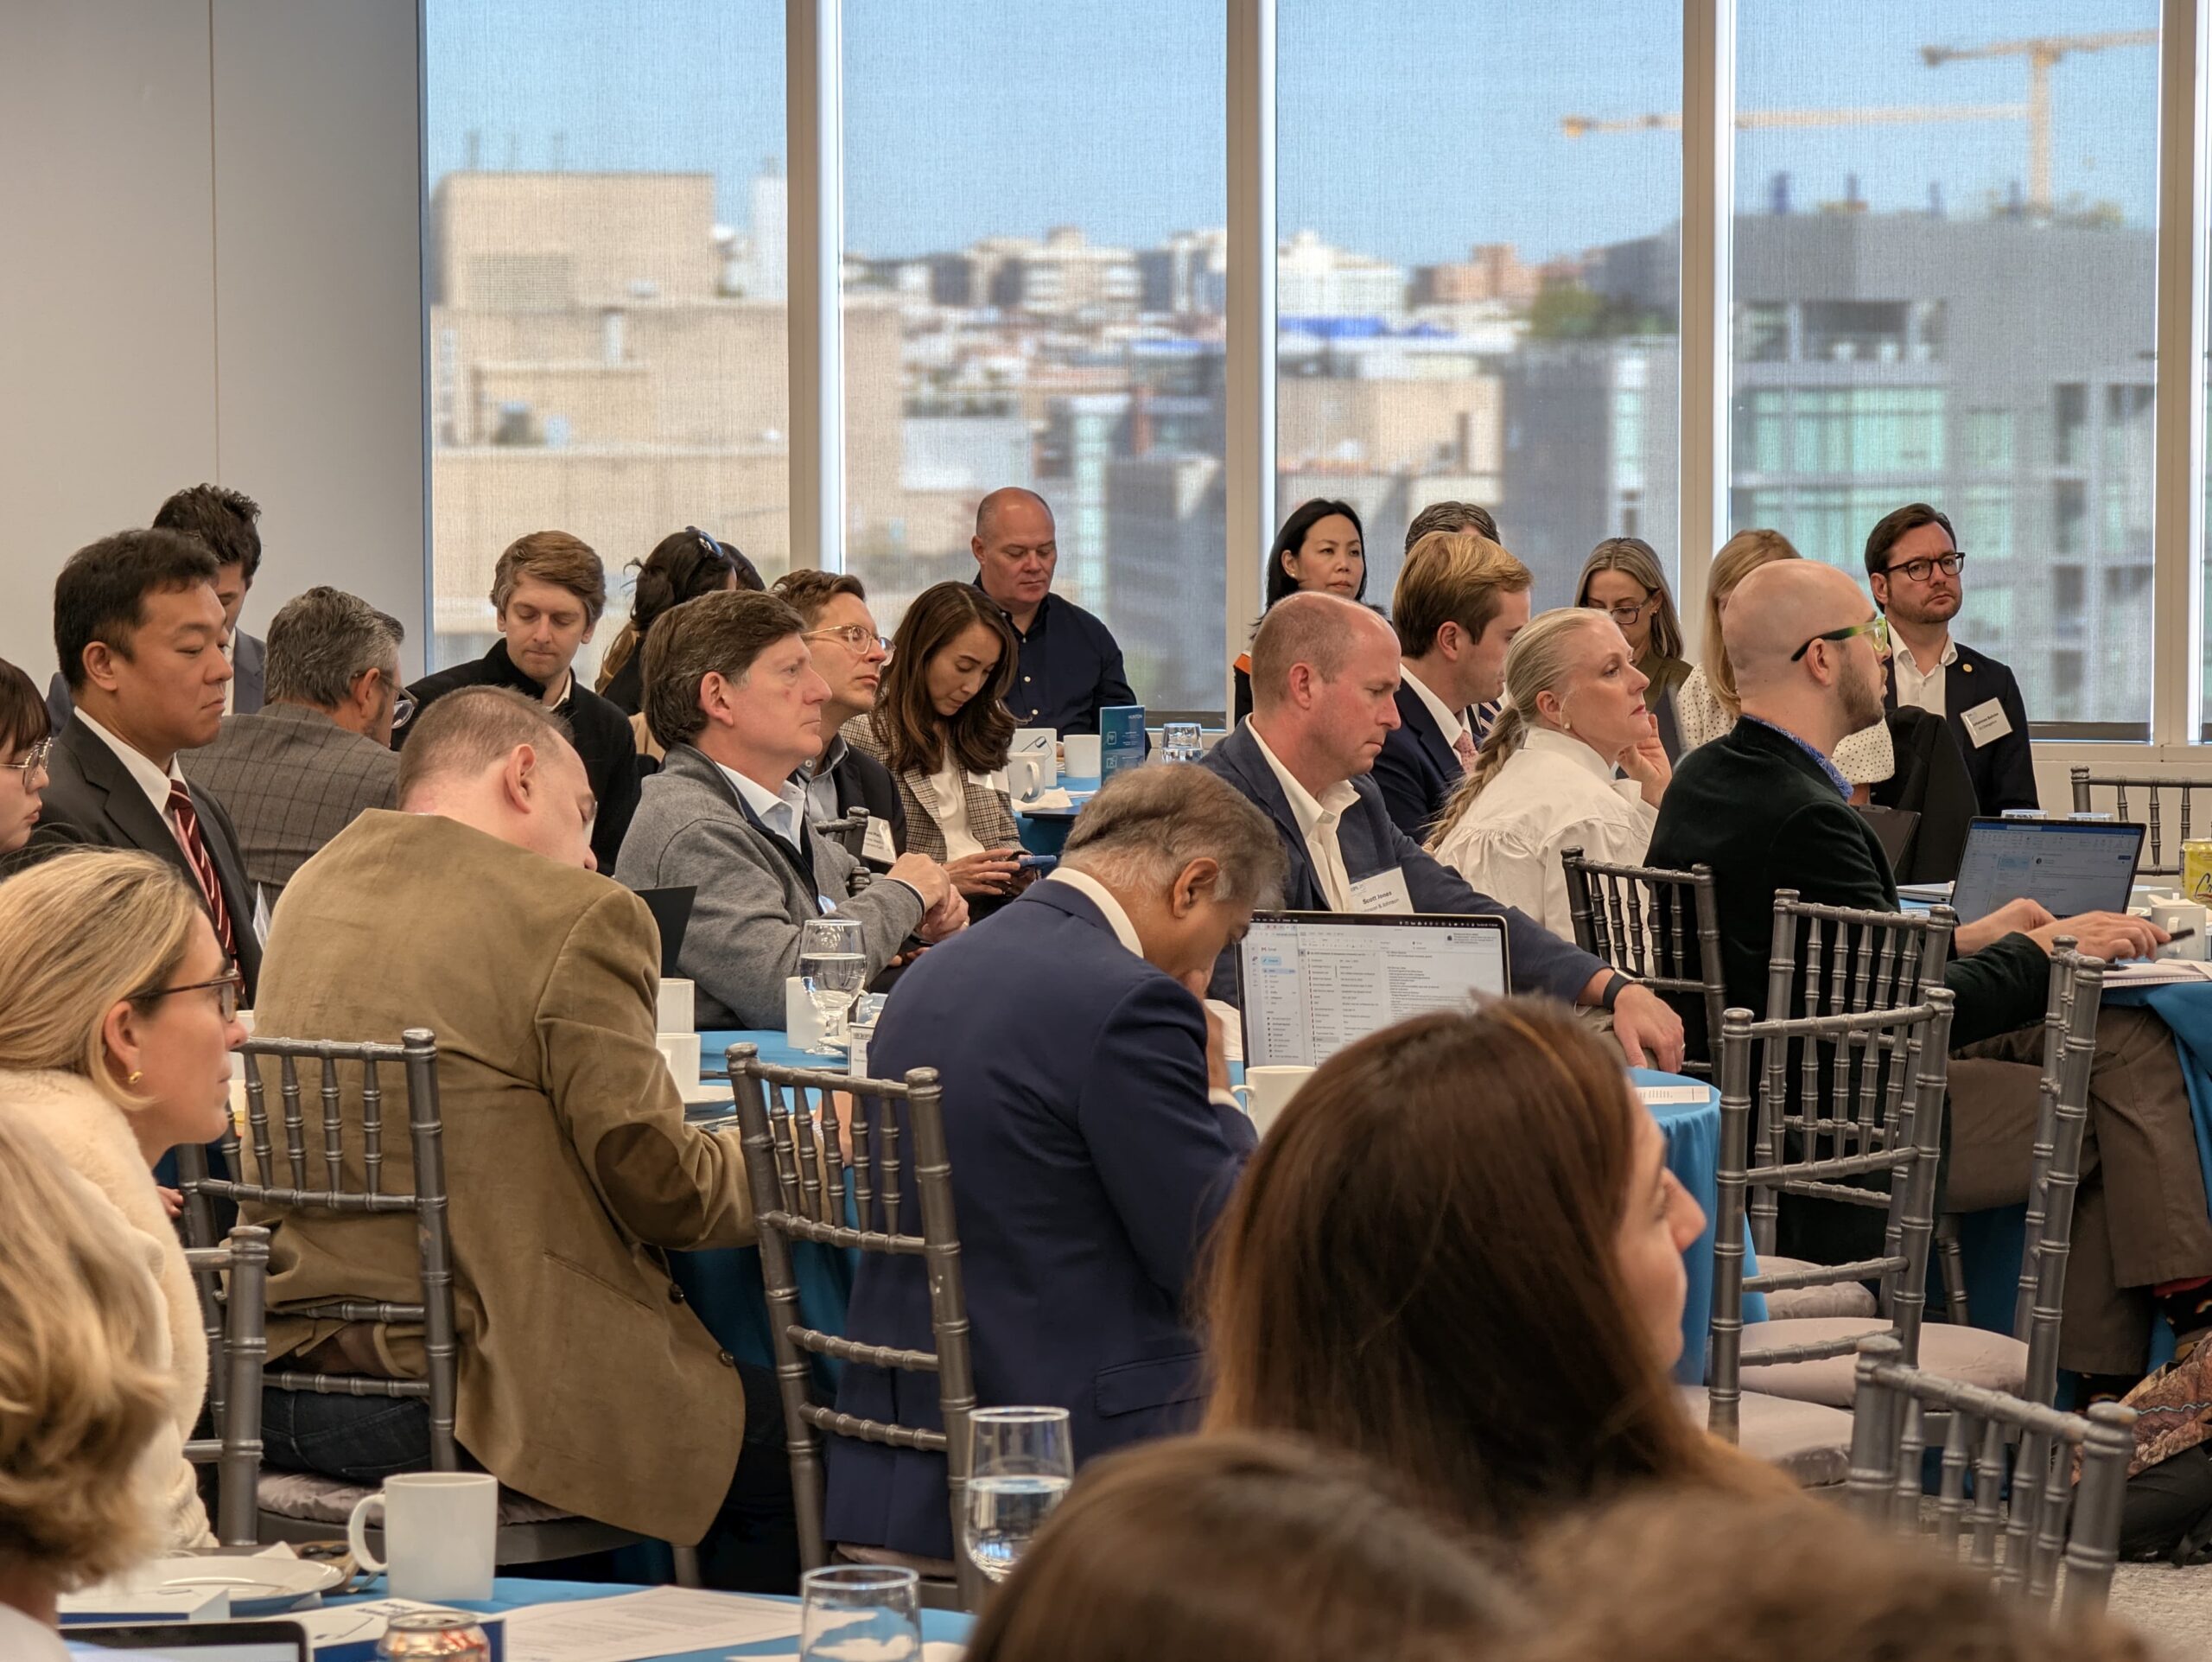
Participants gathered in Washington, DC, with satellite participation in London and Brussels. CIPL members and representatives from regulatory authorities and policymaking institutions around the world joined to discuss the challenges and opportunities shaping data policy, privacy and responsible innovation.
The Summit was a chance to reflect on our progress since 2001 and to exchange perspectives on the issues ahead. It also continued the dialogue between industry and policymakers that has been central to CIPL’s work since our founding.
Below are the highlights from Day One.
Lightning Talks on AI, Innovation, Regulation, Ethics and the Future of Business
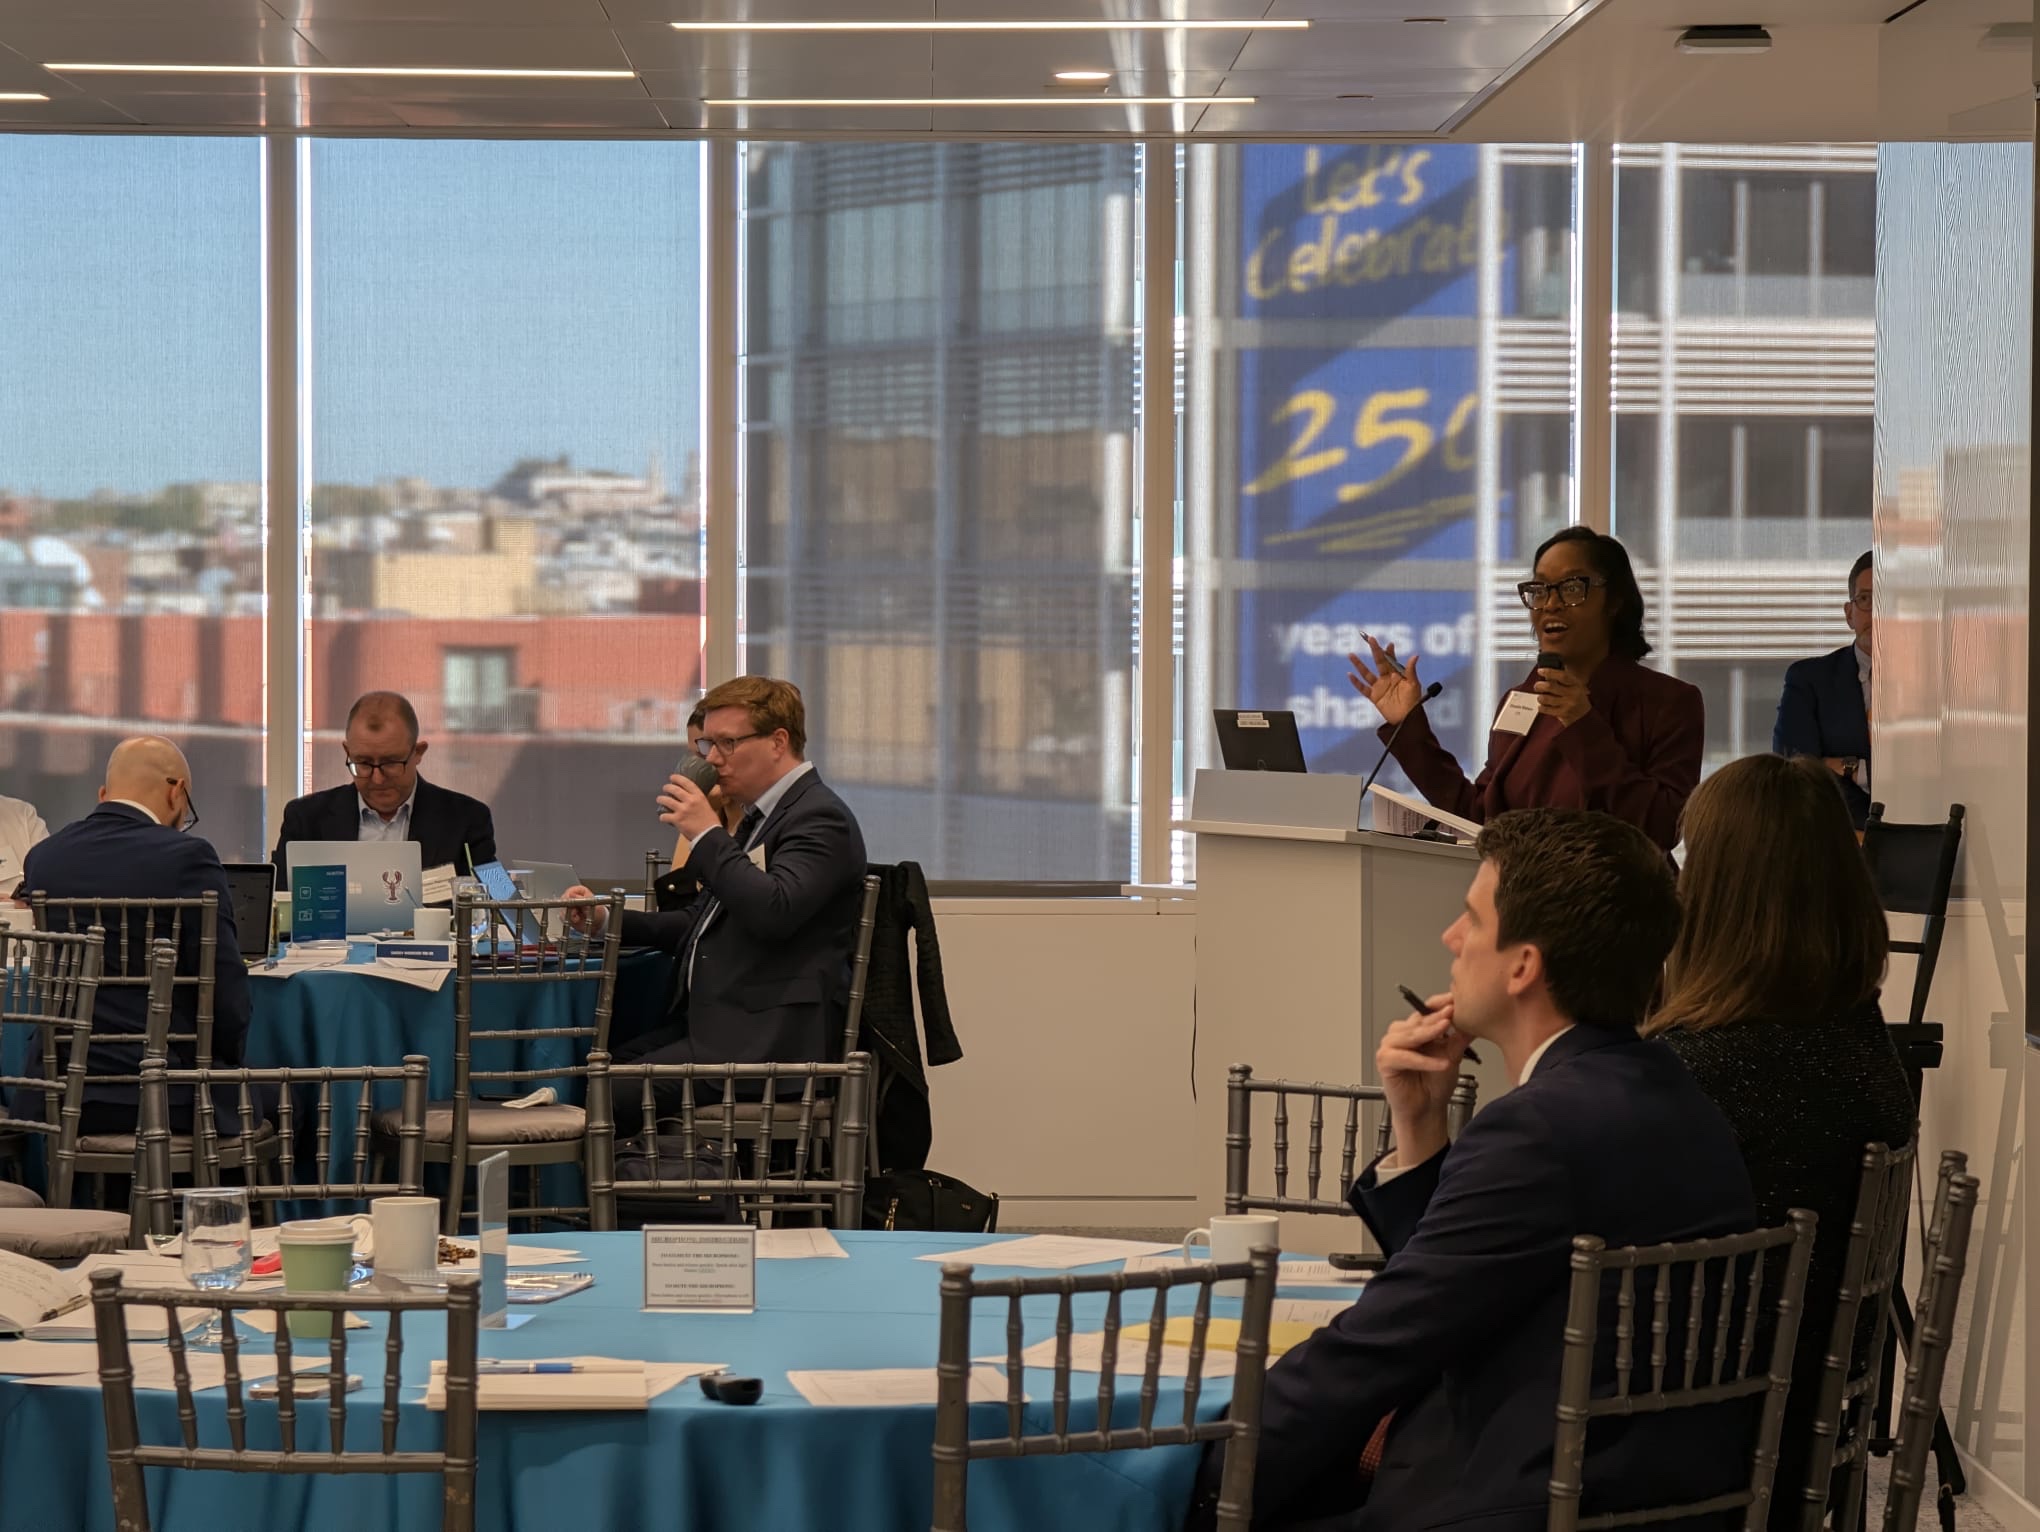
After opening remarks from CIPL President Bojana Bellamy, five leading speakers delivered lightning talks on “AI, Innovation, Regulation, Ethics and the Future of Business”. They shared perspectives on the challenges and opportunities shaping the future of data policy and responsible innovation:
- Russell Wald, Executive Director at the Stanford Institute for Human-Centered Artificial Intelligence (HAI), explored the emerging capabilities of world models, their potential global implications and risks, and the governance frameworks needed to support their responsible development.
- William Malcolm, Executive Director, Regulatory Risk and Innovation at the UK Information Commission’s Office, discussed the evolving and expanding role of technology regulation across the economy. He stressed the importance of collaboration in building trust in the accountable use of technology.
- Luis Héctor Chávez, Chief Technology Officer at Replit, examined how AI is broadening access to software development and empowering domain experts. He also highlighted the growing importance of human judgement and practical safeguards.
- Rob Sherman, Vice President and Deputy Chief Privacy Officer at Meta, reflected on the evolving landscape of data governance. Drawing on key case studies, he examined how meaningful accountability mechanisms and appropriate checks and balances support confidence in AI innovation.
- Pamela Snively, Chief Data & Trust Officer at TELUS, explored the role of trust in ensuring that we achieve the benefits of AI. She highlighted how trustworthiness can and should be embedded into the architecture, design and safeguards of technological systems.
Global Data Policy in the Era of Digital Sovereignty: Impacts on AI, Cybersecurity and Trade
The second session, “Global Data Policy in the Era of Digital Sovereignty: Unpacking Impacts on AI, Cybersecurity, and Trade”, was moderated by CIPL’s Shaundra Watson, CIPP/US, AIGP. The discussion was guided by contributions from:
- Johannes Bahrke (EU Delegation to the United States)
- Christopher Calabrese (Microsoft)
- Anupam Chander (Georgetown Law)
- Kate Charlet (Google)
- Philippe Dufresne (Office of the Privacy Commissioner of Canada / Commissariat à la protection de la vie privée du Canada)
- Bill Guidera (International Trade Administration)
- Halak Shrivastava (Cohere)
Data sovereignty trends are increasing around the world. Governments want to protect national security, economic interests and individual rights, and they are turning to data policy to do so. This limits the flow of data just as advanced AI technologies create demand for more of it.
Against that backdrop, the session sought to clarify current data and digital policy priorities and consider the potential impact on innovation and international trade.
From Digital Trust to Physical Safety: Deploying Responsible Biometric Solutions
After a networking lunch, the afternoon began with “From Digital Trust to Physical Safety: Deploying Responsible Biometric Solutions for Real-World Risk in Online Systems”. The session was moderated by CIPL’s Natascha Gerlach, with insights from:
- Jennifer Abrahamsen (Tools for Humanity)
- Krystal Denley Bowen (Uber)
- Christine Frye (Bank of America)
- Lucia Harris (Match Group)
- Elisa Jillson (FTC)
- Connie LaSalle (NIST)
Digital platforms increasingly shape interactions that have real-world consequences. Risks that originate online, such as impersonation, fraud, harassment or deceptive behaviour, can quickly give rise to offline harm. The discussion addressed how proactive safety measures, particularly those aided by biometric technologies, can coexist within current regulatory frameworks.
Key insights from the session included:
- How to approach safety by design when digital interactions can lead to physical interactions.
- What other sectors can learn from financial services about designing proactive fraud prevention and authentication into digital services.
- An exploration of the practical safeguards that enable responsible deployment of biometric technologies.
- How to make the greatest practical difference in enabling the responsible deployment of biometric technologies.
State of the Union: U.S. Legislative and Enforcement Priorities
The final session of Day One, “State of the Union: U.S. Legislative and Enforcement Priorities”, was moderated by CIPL’s Mark Smith. Speakers were:
- Hanna Abrams, Assistant Attorney General, Maryland
- Alfredo Diaz, Assistant Attorney General, Office of the Attorney General, Florida
- John Eakins, Deputy Attorney General, Delaware
- Michael Macko, Former Head of Enforcement, CalPrivacy
- Sen. James Maroney, Connecticut General Assembly
- Aaron Simpson, Partner, Hunton
- Cooper Vaughan, Senior Counsel to the Director of the Bureau of Consumer Protection, U.S. Federal Trade Commission
U.S. states continue to play a leading role in shaping the regulatory landscape for privacy, cybersecurity, artificial intelligence, consumer protection and children’s online safety, with federal initiatives waiting in the wings. As new laws proliferate and enforcement activity intensifies, organisations must navigate an increasingly complex and fragmented set of state requirements. These shape how data is collected, used, governed and protected.
The panel brought together leading voices from state and federal level to break down this evolving policy and enforcement landscape.
Thank You to Our Speakers and Participants
CIPL thanks all of our speakers, moderators and participants in Washington, DC, London and Brussels for their insights and the lively discussion throughout the day. As we celebrate #CIPLat25, we look forward to continuing the conversation on responsible innovation, data policy and trust with our members and the wider community.
Want to stay up to date with CIPL’s work? Explore our latest publications and upcoming events on the CIPL website.